 DevEdge
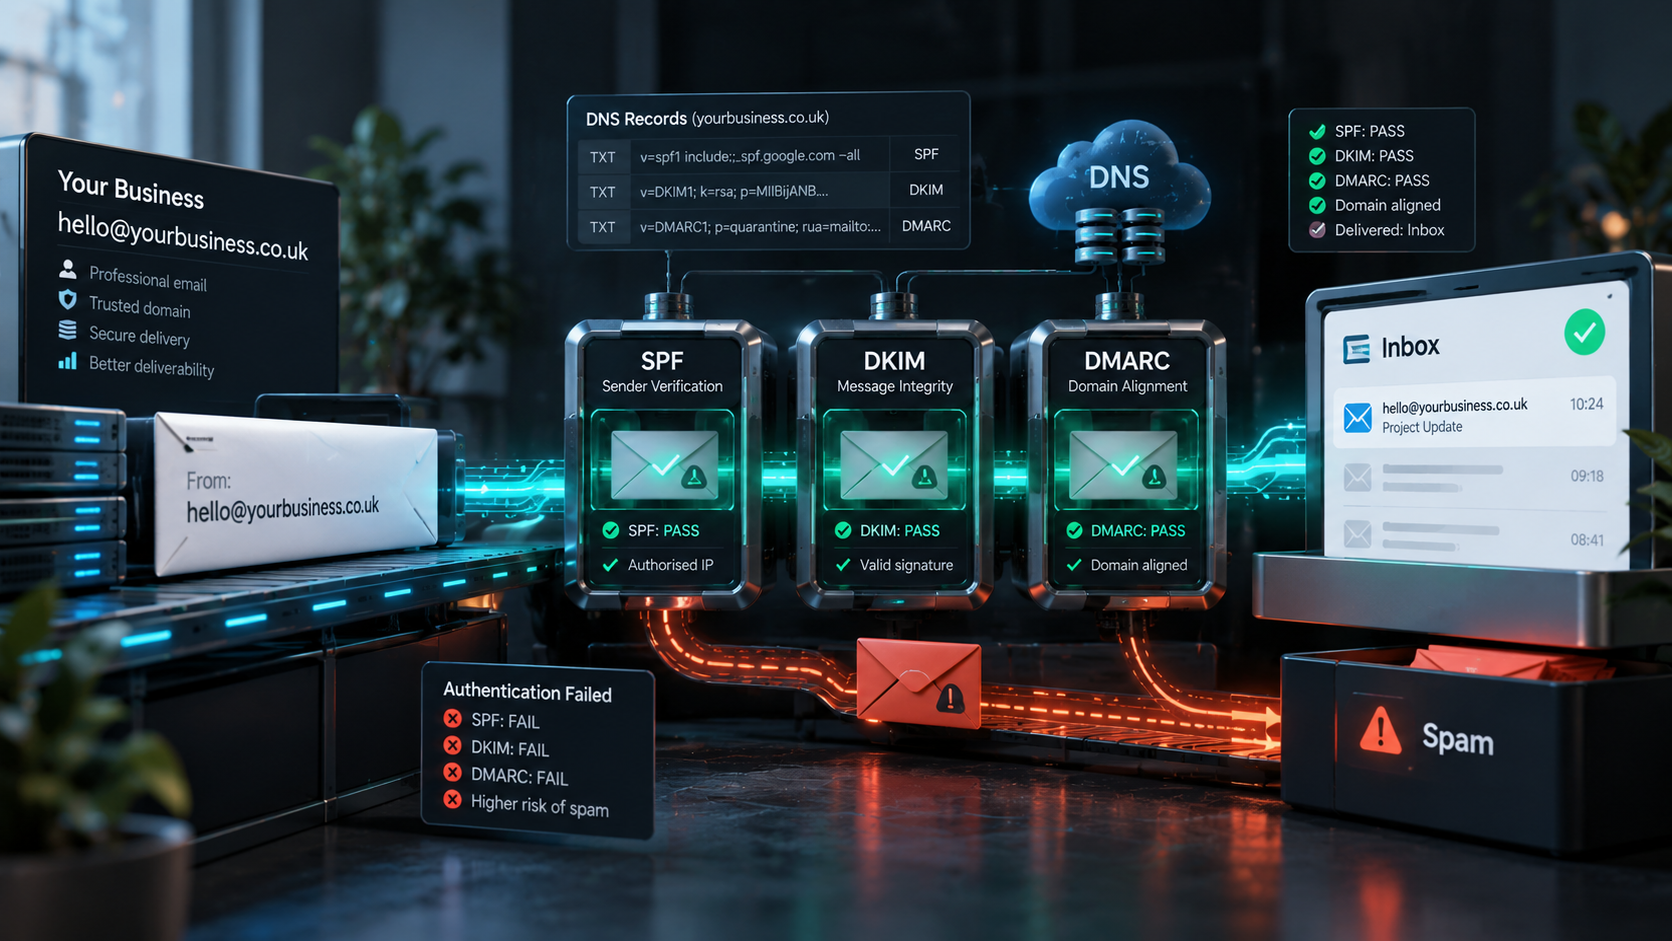
Few things are more damaging to a commercial operation than critical business emails disappearing into a customer’s spam folder. Quotes go unseen, invoices are missed, and routine customer inquiries go unanswered. Yet over the past twelve months, thousands of UK small and medium businesses have experienced an abrupt decline in email deliverability.
The reason is not bad luck; it is a fundamental shift in how global mailbox providers handle incoming mail. Google and Yahoo formally introduced mandatory email authentication requirements for domain owners in early 2024, enforcing strict compliance with established internet standards (RFC 7208 for SPF, RFC 6376 for DKIM, and RFC 7489 for DMARC). If your domain name is not properly authenticated using SPF, DKIM, and DMARC, major receiving servers will flag your messages as suspicious or reject them entirely.
Here is a straightforward, practical explanation of what these three DNS protocols do, why your emails are failing, and how to fix your domain configuration.
The Core Trio: How Email Authentication Works
Email was originally designed in the 1970s with zero built-in security. Anyone could forge an email claiming to be from [email protected]. To combat rampant phishing and spoofing, the internet adopted three complementary verification layers:
1. SPF (Sender Policy Framework): The Authorised Senders List
SPF is a single TXT record published in your domain’s DNS. It acts as a public register listing every IP address and third-party service authorized to send email on behalf of your domain name.
When a receiving mail server receives an email from yourcompany.co.uk, it checks your SPF record. If the email originated from an IP address not included in your SPF record, the email fails the SPF check.
2. DKIM (DomainKeys Identified Mail): The Digital Wax Seal
While SPF verifies the sender’s server IP, DKIM verifies that the email content was not altered in transit. Your sending server attaches a cryptographic digital signature to the email header.
The receiving server fetches your domain’s public cryptographic key from your DNS records to verify the signature. If the signature matches, the recipient knows with mathematical certainty that the email genuinely came from your organization and was not intercepted or modified.
3. DMARC (Domain-based Message Authentication, Reporting, and Conformance): The Policy Enforcer
DMARC is the crucial overarching policy layer. It instructs receiving servers what to do if an email claims to come from your domain but fails SPF or DKIM checks.
Without DMARC, receiving servers must guess whether a failed email is legitimate or phishing. DMARC also provides reporting, sending daily aggregate XML summaries back to your domain detailing every service attempting to send mail in your name.
The Common Mistake: Un-Aligned Third-Party Senders
The primary reason legitimate UK businesses fail email authentication is that modern companies send email through multiple disparate platforms:
- Day-to-day staff email via Microsoft 365 or Google Workspace.
- Website contact forms and order confirmations sent via your WordPress web server.
- Marketing newsletters sent through Mailchimp, Klaviyo, or ActiveCampaign.
- Invoices sent through Xero or QuickBooks.
- CRM notifications sent through HubSpot.
If your SPF record only authorizes Microsoft 365, but your website contact form or Xero sends an invoice claiming to come from [email protected], that invoice will fail SPF alignment and land directly in your customer’s junk folder.
Step-by-Step Guide to Fix Your Domain Authentication
Step 1: Audit All Outbound Sending Streams
Before modifying DNS records, compile an exhaustive inventory of every software tool, server, and platform that sends email using your domain. Missing a single billing or contact form service will cause its emails to be blocked.
Step 2: Construct a Single, Valid SPF Record
A domain must have only one SPF record. Creating multiple TXT records starting with v=spf1 invalidates your SPF configuration entirely. Combine all authorized services into a single string:
v=spf1 include:spf.protection.outlook.com include:_spf.google.com include:sendgrid.net ip4:192.0.2.1 -allNote: SPF has a strict limit of 10 DNS lookups. If you exceed 10 includes, receivers will return an SPF PermError. Consolidate your sending mechanisms to stay within this limit.
Step 3: Generate and Publish DKIM Keys for Every Provider
Log in to each sending service (Google Workspace admin, Microsoft 365 Defender, Mailchimp, your website SMTP provider) and generate a 2048-bit DKIM key. Publish the generated CNAME or TXT records in your DNS management console.
Step 4: Implement DMARC Starting in Monitoring Mode
Never implement a strict DMARC rejection policy on day one. Always start in monitoring mode (p=none). This allows you to collect reports and identify un-authenticated senders without disrupting live communications:
v=DMARC1; p=none; rua=mailto:[email protected]; pct=100; sp=noneReview your reports for 2 to 4 weeks. Once you confirm that 100% of your legitimate email streams pass authentication, graduate your policy to p=quarantine (routes failed mail to spam), and ultimately to p=reject (completely blocks spoofed emails).
Professional Domain and Email Management
Configuring email authentication across complex multi-vendor setups requires technical precision. A single misplaced colon or syntax error in a DNS record can silently halt all corporate communications.
At DevEdge, our domain and business email services ensure your DNS records, mail routing, and authentication protocols are engineered to the highest deliverability standards. If your emails are landing in spam, we can perform a full deliverability audit and restore your sender reputation.
